Description:
CPE Hour: 1
Synopsis
Emerging risks are increasingly interconnected, fast-moving and difficult to contain within traditional organisational boundaries. Cybersecurity remains the highest-ranked global risk and internal audit priority, with AI and digital disruption close behind, while geopolitical uncertainty, resilience, third-party dependencies and regulatory change add further complexity. What these risks share is not their subject matter but their structure: they cut across functions, combine multiple sources of expertise and evolve faster than any single assurance provider can assess them alone. Yet the Three Lines Model is still commonly read as a diagram of separation, designed for risks that were more linear, contained and clearly owned.
The result is a familiar paradox. An organisation can have capable risk specialists, strong second-line functions, a well-resourced internal audit function and a full calendar of reviews, and still leave the board with many reports but no reliable view of the risk itself. Risk registers do not reconcile, rating scales are incompatible, assessment cadences range from continuous monitoring to annual review, and several providers may examine the same visible controls while the interfaces, dependencies and emerging exposures between them remain unexamined. More assurance activity simply generates more fragments. In practice, the problem is rarely the absence of expertise; it is the absence of an architecture that connects expertise without blurring accountability. Independence, meanwhile, is too often interpreted as a reason for organisational distance rather than as a standard of professional judgement.
This session argues that the lines remain necessary but are no longer sufficient, and offers a way forward that does not require abandoning the Three Lines Model. Lines without links produce fragmentation; links without lines produce ambiguity. Vertical accountability therefore needs to be crossed by horizontal links of knowledge. Each link requires its own safeguard, because management must retain ownership of the risk and the response, while internal audit must retain its objective judgement and accountability for its conclusions. Integration here means disciplined connection, never role blending.
Participants will also take away a more useful test of objectivity than physical distance, built around documented advisory terms, named decision-makers, appropriate safeguards and transparency with the board, together with a realistic four-stage path from parallel work to adaptive integrated assurance. Maturity will differ by risk within the same organisation: highly interconnected and rapidly evolving risks may require deeper integration than stable, well-understood exposures. Reaching the highest stage everywhere is therefore neither necessary nor desirable. The objective is not maximum integration, but the right degree of connection for the risk.
Speaker
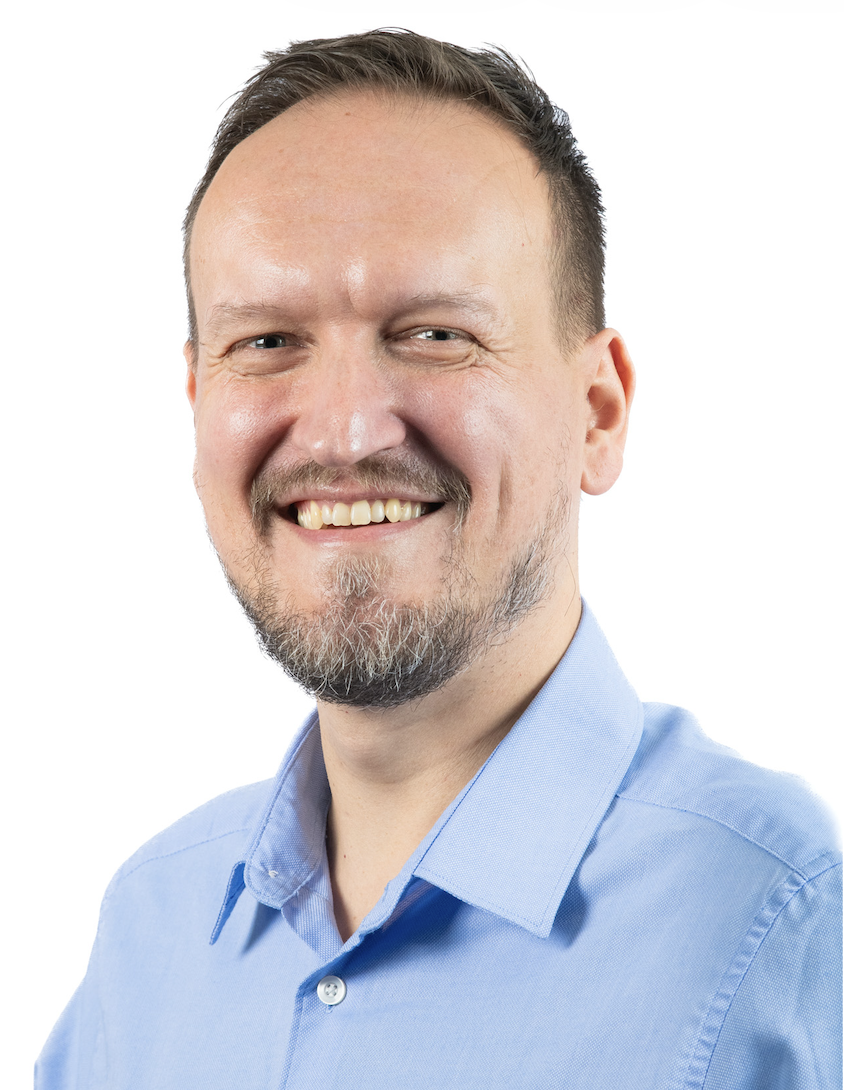
Dr. Matej Drascek
President
IIA Slovenia
Dr Matej Drascek is an international speaker and author specialising in internal audit and ethics. His recent book, 'Ethical Decision-Making in Management,' has been published by Routledge, New York. He has served as a lecturer for various universities and faculties. He has contributed numerous professional and scientific articles on topics such as internal audit, business ethics, and strategic management.
Dr Drascek is a sought-after speaker at both domestic and international conferences, where he shares new tools and insights in internal audit, strategic risks and business ethics. His contributions have been recognised, including receiving The IIA’s John B. Thurston Award for the best article about business ethics.
Currently, he serves as the President of IIA–Slovenia. Holding a PhD. in Business Ethics from the University of Ljubljana, Slovenia, Dr. Drascek holds certifications, including CIA, CRMA, CFSA, CFE, CC, and CSF-X.
Registration Fees
Free for IIA/ISACA Singapore* members and S$35 for non-members.
*For IIA Affiliate/ISACA Singapore members, kindly input the promo code "OCT26" to enjoy discounted registration rate.
Payment by Credit Card or PayNow/PayLah! transfer
Make the payment of your registration fees via PayNow/PayLah! transfer by following the steps below:
- Upon completing your registration, proceed to payment and select the “Pay Later” option to complete your registration.
- Login to Internet Banking or Mobile Banking.
- Scan our corporate PayNow/PayLah! QR code.

4. Verify our UEN number (S76SS0058D) and release funds.
NOTE: Kindly include the details below under the UEN/Bill Reference Number (text limit of up to 25 characters).

5. Once payment is made, please print screen the transaction and email to events@iia.org.sg for our tracking purposes. Please include in your email the Event Code of each event when you are making payment of registration fees for multiple events in a single transaction.
Please refer to PayNow and PayLah! for more information.
Terms and Conditions:
- Registration is on a first-come-first-served-basis.
- Only online registrations are accepted. All registrations must "Proceed to Payment" to complete registration. Full payment must be received prior to the webinar commencement. Upon completion of successful registration, you should receive an auto-generated registration confirmation via email.
- No refund will be made for any cancellations made after successful registration or non-attendance on the actual date. A substitution (of the same membership category) is allowed at no additional charge, if advised in writing.
- A reminder will be sent 1 day prior to the talk.
- IIA Singapore reserves the right to revise the programme as necessary.
- IIA Singapore reserves the right to publish or use for any other purpose whatsoever deemed appropriate, for all images taken by the official photographer(s) during the event.
PLEASE NOTE:
A system generated email will be sent upon successful registration of the above mentioned event. If you do not receive the email notification, please call IIA Singapore at +65 6324 9029. |